Reviewing the campaign the way its victims would have met it makes one thing obvious: nothing about it looked like a scam. The ad carried a blue verified check. It came from u/hbomax, an account with a real posting history in official HBO Max communities. The landing page copied the streaming service's fonts, pricing tiers, and legal disclaimers closely enough to survive a quick glance. Running the payload inside an isolated sandbox rather than a live machine, the "download" turned out to be no download at all, only a command waiting to be pasted. That is the whole trick, and it is why this one deserves a close read.
Between September 15 and 17, 2026, security teams at Hudson Rock and ADAMnetworks documented what they named PasteSwitch, a cross-platform operation that briefly hijacked HBO Max's verified Reddit advertising account. For roughly 48 hours, that account pushed malicious ads that funneled clickers toward fake pages and a self-inflicted malware install. What follows is a verified breakdown built from those researcher reports, coverage in TechCrunch, AdExchanger, McAfee, and Malwarebytes, and the original Reddit thread from the user who spotted it first.
The scam at a glance
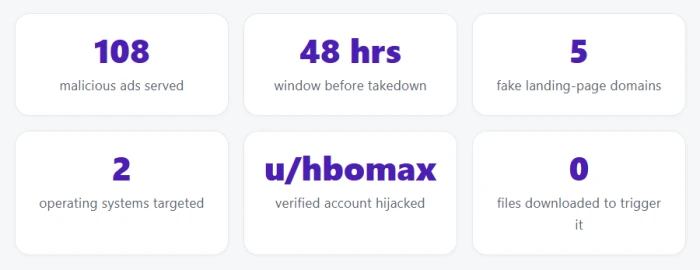
The one-line version Attackers took over a trusted, verified brand account, wrapped a known social-engineering technique called ClickFix in professional HBO Max branding, and let the trust of the checkmark do the persuading. Victims were guided to run the malware themselves.
How the scam actually worked
Strip away the branding and the mechanics are a five-step chain. Each step was designed to lower a specific guard that a cautious user would normally raise.
| Compromise a verified accountThe crew gained control of an HBO Max account authorized to buy ads on Reddit. How the account was taken over has not been disclosed by HBO, Warner Bros. Discovery, or Reddit. |
| Run polished ads at scaleUsing that account, they published 108 ads across a two-day window. The verified badge and genuine posting history made the ads read as official brand promotions rather than obvious traps. |
| Route clicks to a lookalike pageAds pointed to domains such as hbomaxx[.]us, a page built to mirror HBO Max branding, pricing, and disclaimers, complete with a join and download button. |
| Swap the download for a commandInstead of an installer, the page displayed a "Get HBO Max" pop-up that walked visitors through opening Terminal (macOS) or the Run box and PowerShell (Windows) and pasting in a supplied command. |
| Let the victim infect themselvesBecause the user runs the command manually using trusted system tools, the payload sidesteps many browser and endpoint protections built to catch file-based downloads. |
Why it slipped through ClickFix works because the malicious step is disguised as a routine fix: a bot check, an app install, an error resolution. No suspicious file lands on disk at the moment of the click, so the usual download warnings never fire. The person becomes the delivery mechanism.
Real page versus fake page
The lookalike did not need to be perfect. It only needed to survive the few seconds between a click and a paste. Here is where the copy diverged from the original.
✅ The genuine HBO Max
Official domainApp store installs
Distributes apps only through official app stores and its own verified site. It has never shipped a native macOS desktop client, so any "Mac app for HBO Max" is a red flag on its own. No legitimate app asks you to paste a command into Terminal to install it.
⚠️ The impostor page
hbomaxx[.]usTerminal command
Copied branding, pricing, and legal text closely, advertised a nonexistent macOS HBO Max app, and offered a join or download button. The final step replaced installation with a copy-and-paste command, the moment the infection actually began.
Case study: the user who caught it first
This campaign was not stopped by an automated threat scanner. It was stopped by one alert Reddit user, posting to the r/cybersecurity community under the flair "Personal Support & Help!" That account, u/Unhappy-Capital-1464, is effectively the first-person record of how the scam met a real person and failed.
The user's first instinct was the right one: assume the account name is faked. Rather than trust the badge, they checked the more common explanation, a lookalike handle using swapped characters.
I did consider some sort of character substitution in the username but clicking it took me to the profile. u/Unhappy-Capital-1464, on ruling out a spoofed handle |
That check is what escalated the finding from "probably a fake account" to "a genuine, verified account has been taken over." The user then examined the destination, hbomaxx[.]us, which they described as looking somewhat legitimate with a join and download button. When the page produced the paste-this-command step, they recognized the pattern immediately.
The classic infostealer / clickfix paste this command to download. u/Unhappy-Capital-1464, describing the payload step |
Crucially, they did not run it. The command was tested inside a sandbox so its behavior could be inspected without executing on a live system, and then the account was reported directly to both Reddit and HBO. That report reached the r/cybersecurity community, which put it in front of the researchers who mapped the full operation.
The takeaway from the one person who met it Three habits defused the entire attack: distrust the badge and verify the profile, treat any "paste this command" step as hostile by default, and report suspicious brand activity to both the platform and the brand.
What the malware actually did
The paste command was only the trigger. What ran afterward depended on the victim's device, and the operation switched payloads accordingly. This is the part most reporting glossed over, so here is the verified breakdown.
| Platform | Technique observed | Payload | What it targets |
|---|---|---|---|
| macOS | Base64-encoded command pulled a payload from ember-bridge[.]com | MacSync plus an "AMOS helper" tied to Atomic macOS Stealer | Browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS keychain passwords, with persistence for further tasking |
| Windows | MP3/HTA polyglot file created a scheduled task, launched 32-bit PowerShell, and disabled the Antimalware Scan Interface | Amatera Stealer, loaded directly into memory | Saved passwords and browser data, harvested without ever writing the stealer to disk |
| Crypto users | Clipboard hijacking and fake wallet apps served based on visitor profile | AnimateClipper and ZigClipper, plus counterfeit Ledger, Trezor Suite, and Exodus apps | Cryptocurrency transfers and wallet recovery phrases |
The reason researchers named it PasteSwitch is that same backend behavior: a single infrastructure that switched between campaigns, platforms, and payloads depending on who clicked. A Mac user, a Windows user, and someone with a crypto wallet installed could click the same style of ad and receive three different attacks.
HBO Max was bait, not the whole net
The streaming brand was the headline, but only one of five lures. The same operation pointed ads at fake AI and developer tools and Mac cleanup utilities, extending its reach far beyond people shopping for a streaming app.
| Fake domain | Ads counted | What it posed as |
|---|---|---|
| hbomaxx[.]app | 40 | HBO Max download |
| codex-craft[.]com | 36 | AI / developer tool |
| apple.clean-disk-guide[.]com | 15 | Mac disk cleaner utility |
| code-desktop[.]com | 11 | Developer software |
| hbomax-macos[.]com | 6 | Native macOS HBO Max app |
Counts as documented by Hudson Rock and ADAMnetworks across the tracked 48-hour window, alongside the hbomaxx[.]us lure that first drew attention.
Who got hurt, and what is still unknown
Here honesty matters more than a dramatic number. Reddit locked the account and removed the ads, but has not disclosed how many people clicked or how many devices were ultimately compromised. That gap is the most important unanswered question in the whole case.
What is confirmed
- 108 malicious ads ran from the verified u/hbomax account.
- The payloads were live and functional across macOS and Windows.
- The first documented person to encounter it recognized the trap and avoided infection.
What has not been disclosed
- How the u/hbomax account was compromised.
- How many users clicked the ads or ran the command.
- Whether other HBO or Warner Bros. Discovery accounts were touched.
Industry analysts made a sober point about timing: this account was caught within two days largely by luck. Advertising accounts on platforms that owners check less often can sit compromised and quietly productive for far longer before anyone notices. Anyone who pasted the command during that window would not have seen an obvious failure. The stealer runs quietly, which is precisely the danger.
Red flags this scam left in plain sight
Every convincing scam still leaves seams. These were visible before any command was pasted.
- A verified brand account promoting a product that does not exist, in this case a native macOS HBO Max app.
- A domain that is close but not exact: hbomaxx[.]us and hbomaxx[.]app instead of the official address.
- An install flow that routes you to Terminal, PowerShell, or the Run box.
- A "verify you are human" or "finish your download" step that ends in copying a command.
- Urgency and polish combined: a professional page pushing you to act in the moment.
If you pasted the command
Recognizing the mistake early limits the damage. The right sequence assumes credentials are already exposed.
- Disconnect and scanTake the device offline and run a full scan with an up-to-date real-time security tool that includes web protection.
- Change passwords from a clean deviceReset passwords for email, banking, and any saved logins using a different, trusted device, not the possibly infected one.
- Turn on multifactor authenticationAdd MFA everywhere it is offered so stolen passwords alone are not enough to log in.
- Move crypto if a wallet was on the deviceAssume recovery phrases and clipboard activity were exposed, and transfer funds to a freshly generated wallet.
- Watch for reuseMonitor accounts for unfamiliar logins and treat any saved session as potentially hijacked.
How the companies responded
Reddit Reddit confirmed that an HBO Max account authorized to run ads had been compromised and used for malicious links. The company said it locked the account, removed the ads, began working with HBO Max to strengthen account security, and noted that no other advertising accounts appeared to be affected.
HBO Max and Warner Bros. Discovery As of publication, HBO and parent company Warner Bros. Discovery had not responded to reporters' requests for comment, and had not explained how the verified account was taken over.
Final verdict
After tracing this one end to end, from the verified badge to the sandboxed payload, the lesson lands harder than the headline suggests.
The scam was not clever in a technical sense. ClickFix is a known technique, the lookalike page was ordinary, and the malware families were already documented. What made it dangerous was borrowed trust. A verified checkmark on a real corporate account did the persuading that the attackers could never have done on their own, and it turned a routine-looking ad into the most convincing part of the con.
The single most useful habit this case rewards is boring and reliable: no legitimate app on any platform will ever ask you to paste a command into Terminal, PowerShell, or a Run box to install it. That rule alone would have stopped every version of this attack, on every device, regardless of how polished the page looked or how trusted the account appeared. Treat a verified badge as a starting point for suspicion, not the end of it, and treat any copy-and-paste install step as an attack until proven otherwise.
The person who caught this did nothing exotic. They doubted the badge, checked the profile, refused to run the command, and reported it twice. That is the entire defense, and it is available to everyone.